Software Supply Chain Security
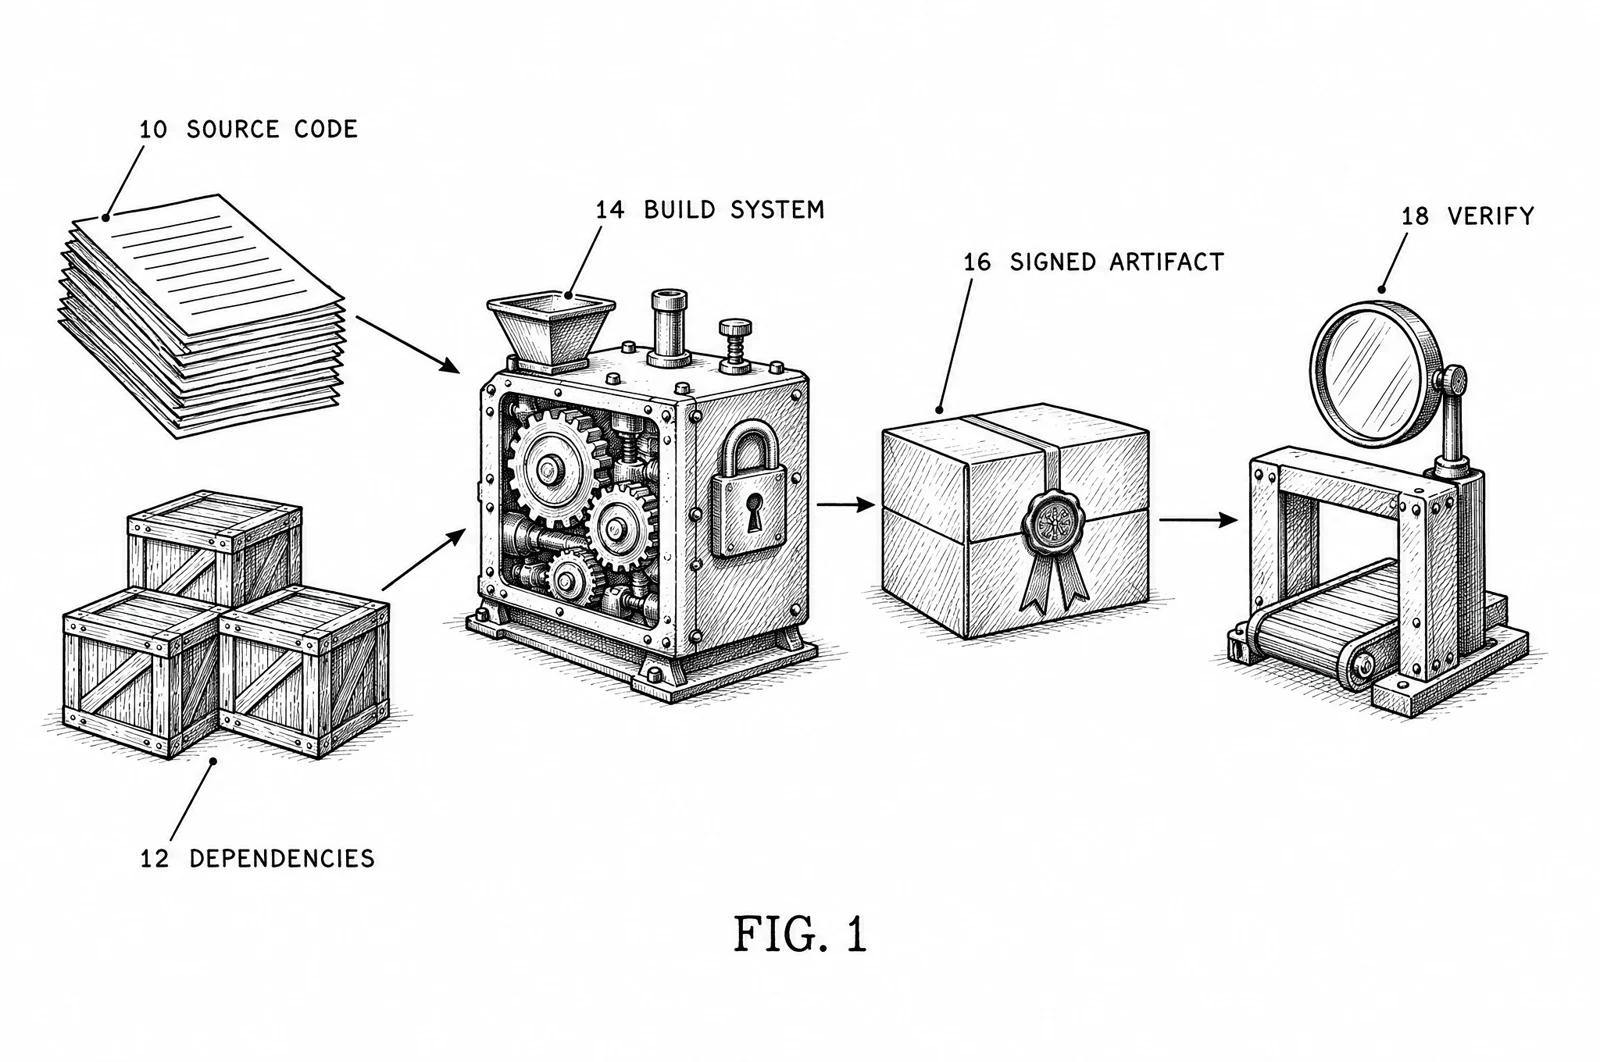
Software Supply Chain Security is the practice of protecting everything that goes into building and delivering software: source code, third-party dependencies, build systems and the final artifacts. It guards against an attacker who tampers with one of these steps (for example, by slipping malicious code into a library). Common measures are strict access controls, signed artifacts, dependency scanning, and provenance records that show which inputs and steps produced a release.
See also SSL, Vulnerability Scanning, Zero Trust, Active Directory, DAST (Dynamic Application Security Testing), Distroless Image.