Kubernetes Secret
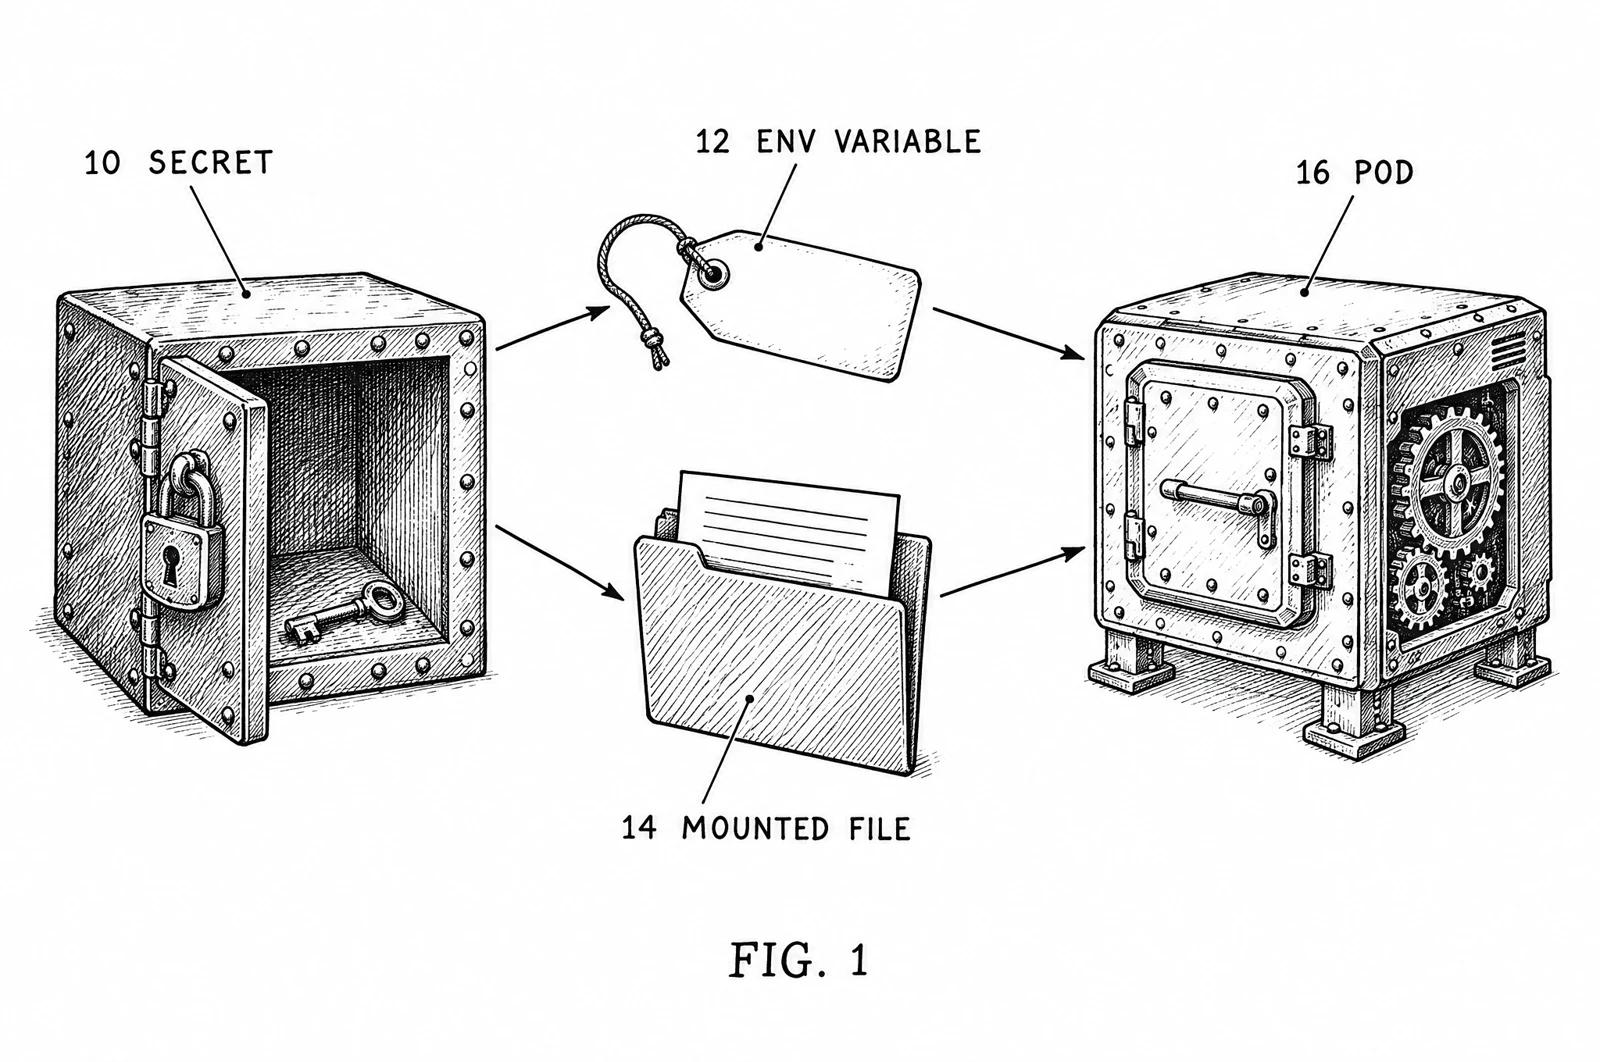
A Kubernetes Secret is an object that stores a small piece of sensitive data, such as a password, an API token or a TLS certificate. Pods read it as an environment variable or as a mounted file, so the value stays out of the container image and the code. The values are only base64-encoded by default, so you should turn on encryption at rest and restrict who can read them.