Kubernetes RBAC
Authentication and Authorization
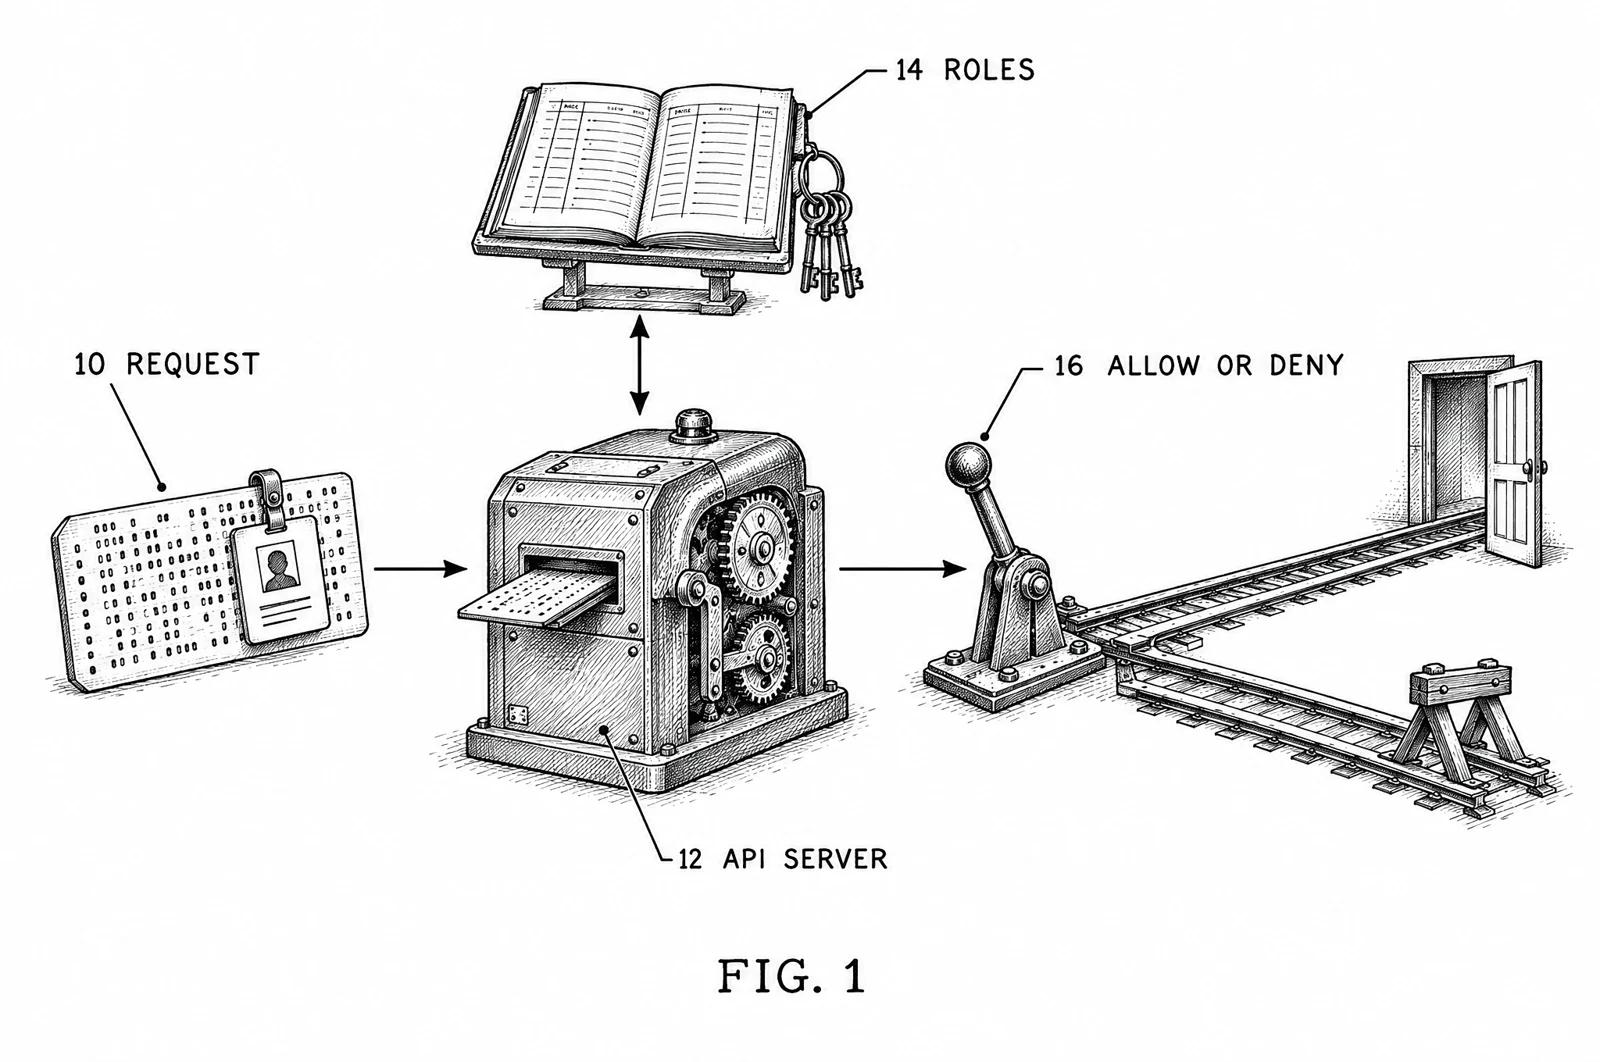
Kubernetes RBAC (Role-Based Access Control) is the system that decides which users, groups and service accounts may do what through the Kubernetes API. A Role or ClusterRole lists allowed actions on resources (for example, get and list on Pods), and a RoleBinding or ClusterRoleBinding gives that role to someone. The API server checks every request against these rules and rejects any request that no rule allows.
See also Kubernetes Role, Kubernetes RoleBinding, Kubernetes ServiceAccount, OIDC (OpenID Connect), SAML (Security Assertion Markup Language), AWS IAM Role.