Kubernetes ServiceAccount
Authentication and Authorization
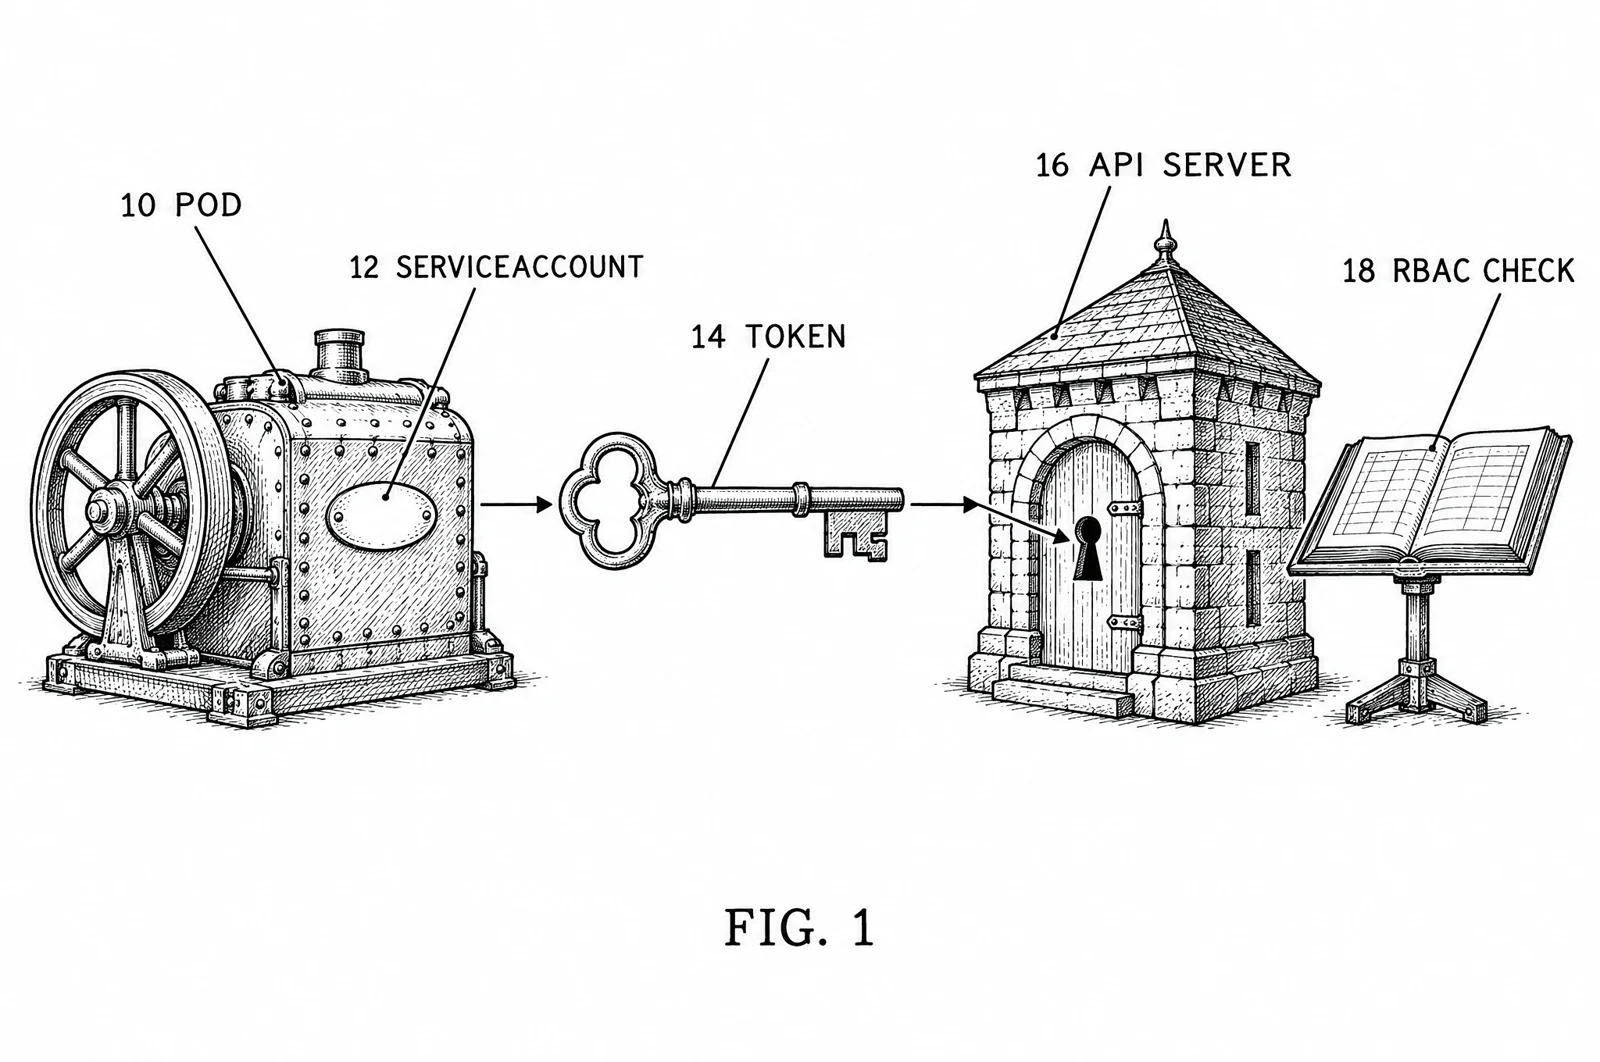
A Kubernetes ServiceAccount is an identity for a pod, the way a user account is an identity for a person. Kubernetes places a short-lived token inside the pod, and the application presents that token when it calls the Kubernetes API. The API server uses it to tell who is calling, then checks role-based access control (RBAC) rules to decide what that identity may do (for example, read 1 ConfigMap).
See also OIDC (OpenID Connect), SAML (Security Assertion Markup Language), AWS IAM Role, AWS STS AssumeRole, Kubernetes ClusterRole, Kubernetes ClusterRoleBinding.