Software Bill of Materials (SBOM)
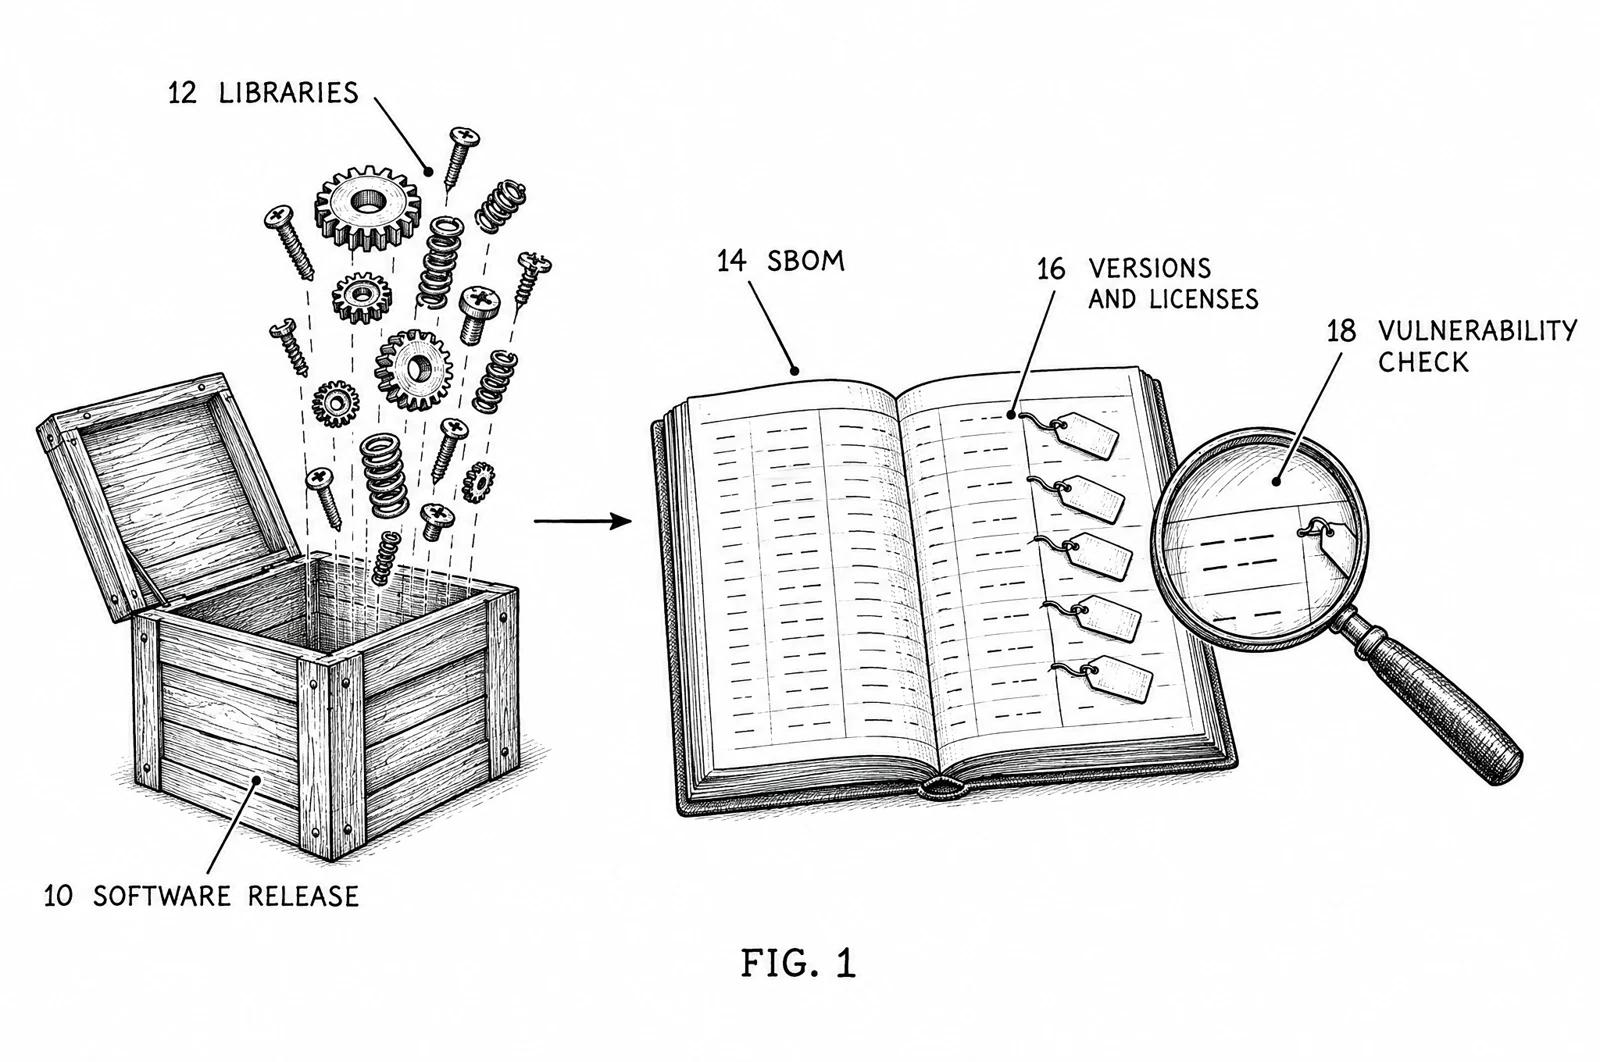
A Software Bill of Materials (SBOM) is a structured list of every component that goes into a piece of software. It records each library, package and container layer with its name, version, supplier and license, usually in a standard format such as SPDX or CycloneDX. When a vulnerability is announced (for example, in Log4j), you search your SBOMs to find which applications contain the affected version.
See also Software Supply Chain Security, SSL, Vulnerability Scanning, Zero Trust, Active Directory, DAST (Dynamic Application Security Testing).