OIDC (OpenID Connect)
Authentication and Authorization
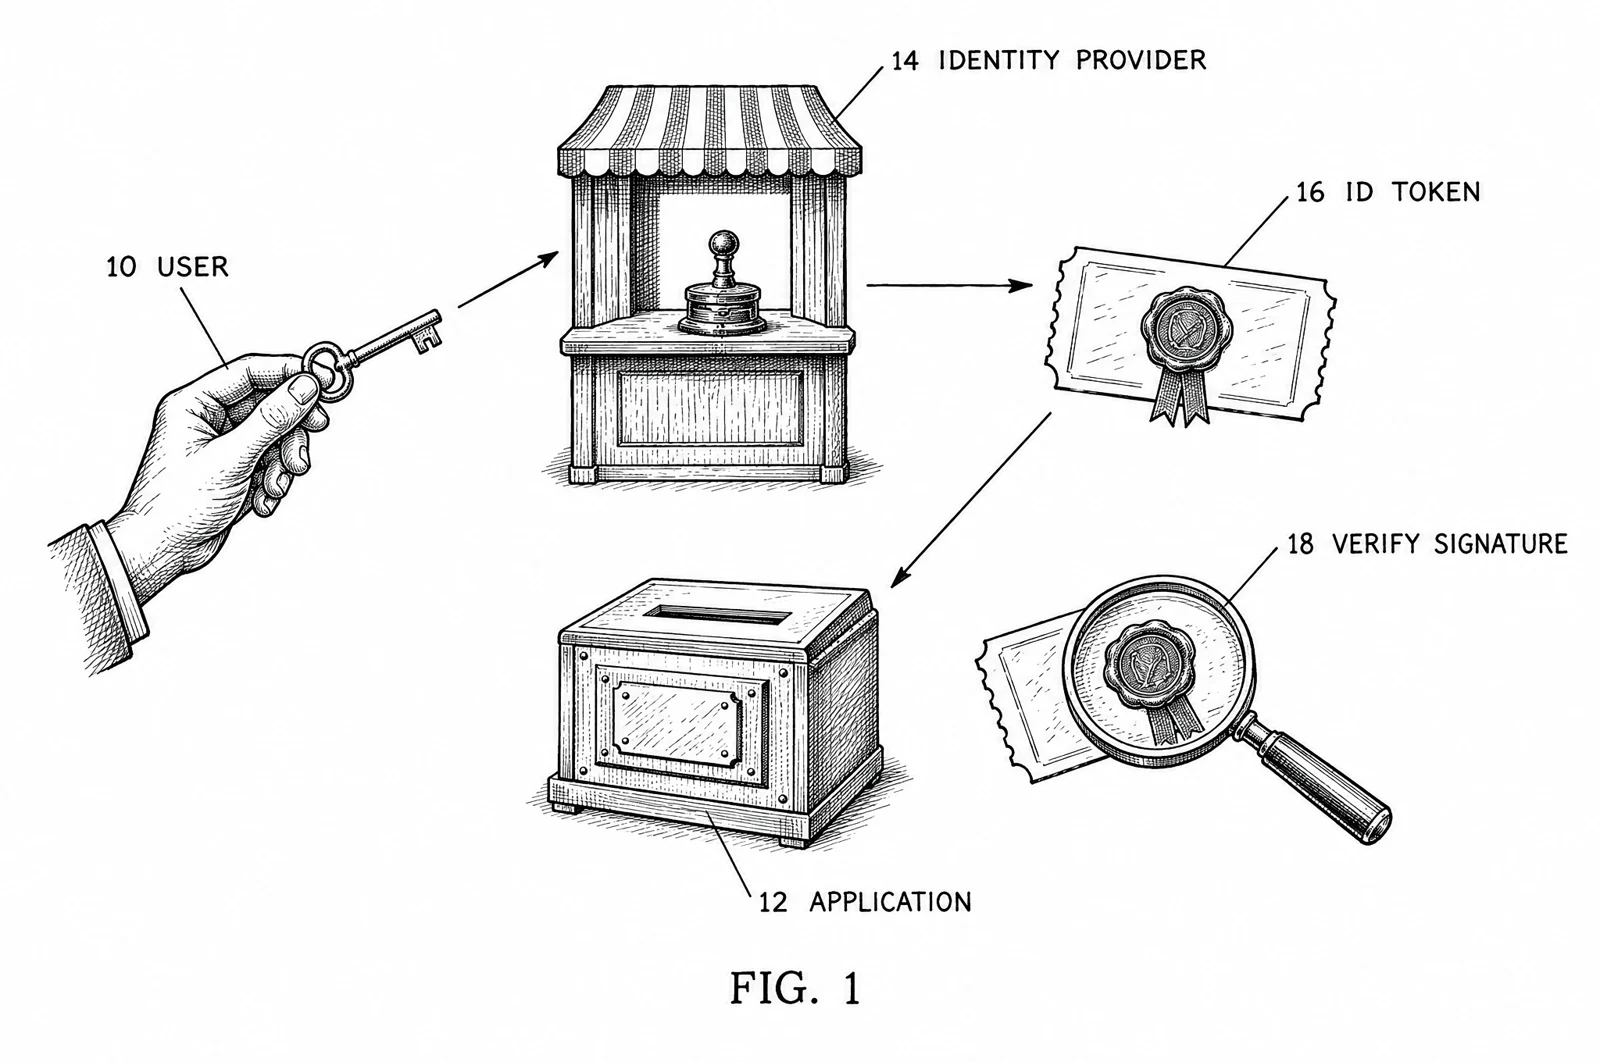
OIDC (OpenID Connect) is a standard way for an application to confirm who a user is by relying on a separate identity provider. It is built on top of OAuth 2.0. The user signs in with the provider (for example, a company login page), and the application receives a signed ID token that states who the user is. The application verifies the signature and trusts the result.
See also SAML (Security Assertion Markup Language), AWS IAM Role, AWS STS AssumeRole, Kubernetes ClusterRole, Kubernetes ClusterRoleBinding, Kubernetes RBAC.