DAST (Dynamic Application Security Testing)
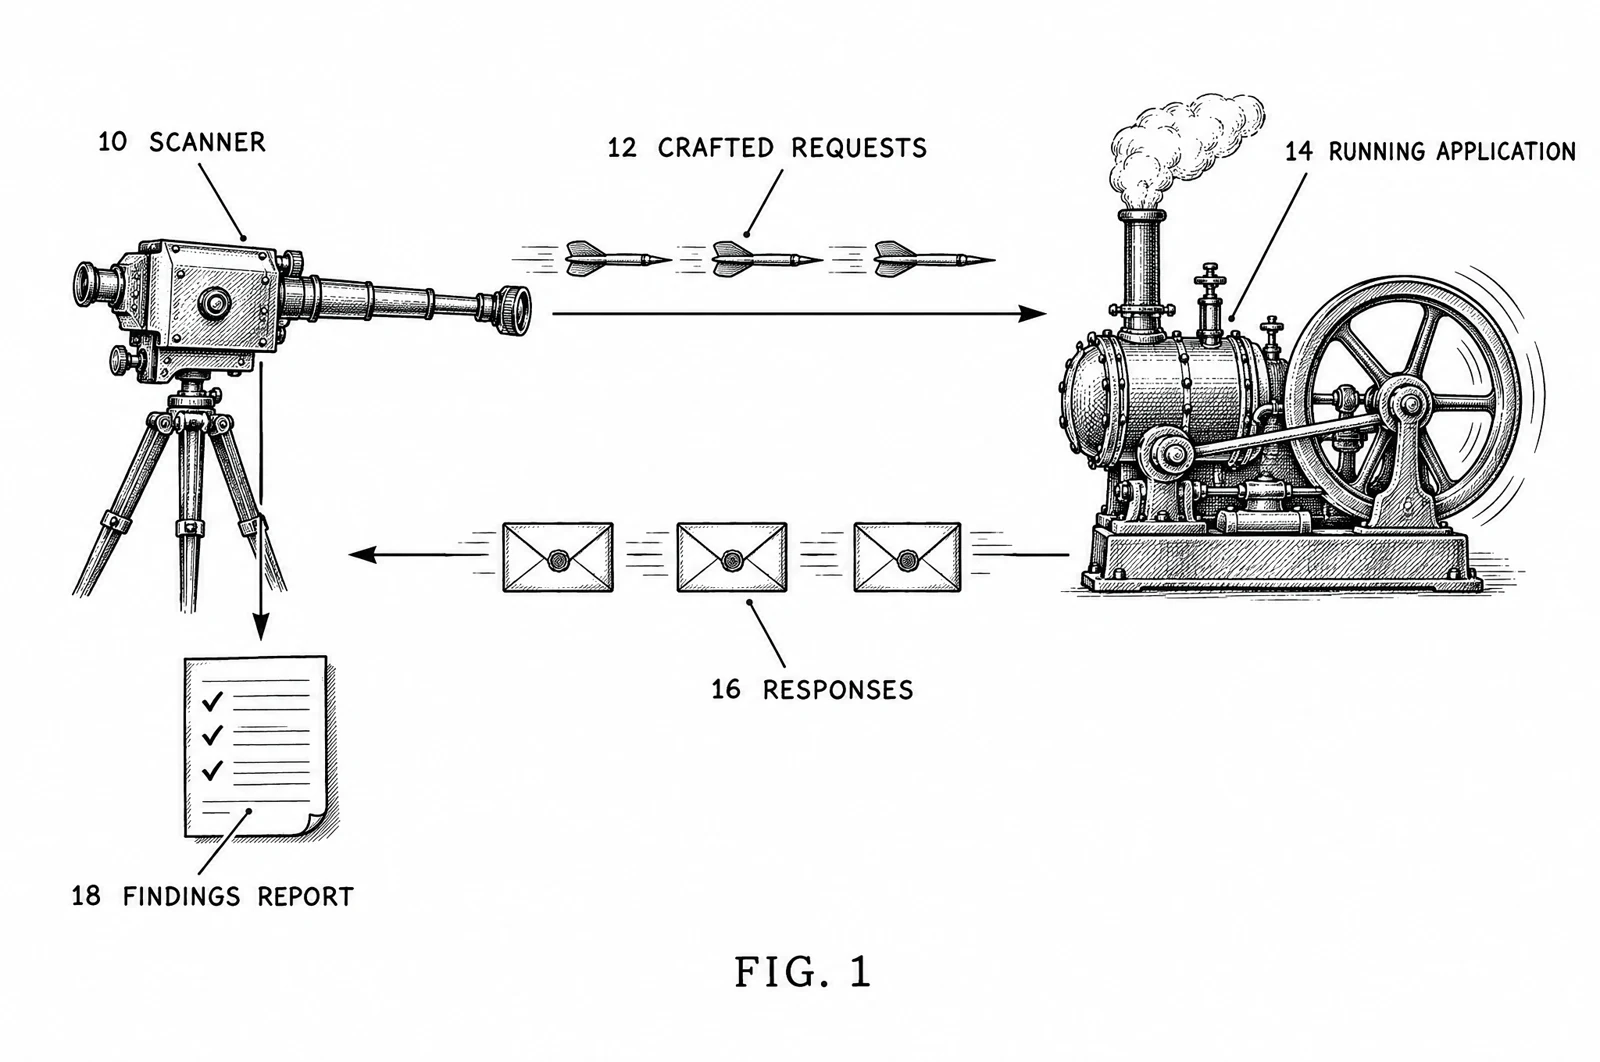
DAST (Dynamic Application Security Testing) is a way to test a running application for security holes from the outside, the way an attacker would. A DAST tool crawls the application to find its pages and endpoints, sends requests with unexpected inputs (for example, a login form filled with database commands), and reads the responses. It needs no source code, and it reports the weaknesses it finds.
See also Distroless Image, Kubernetes Pod Security Admission, Kubernetes Pod Security Standards (PSS), Kubernetes SecurityContext, Linux Kali, Mutual TLS (mTLS).