AWS IAM Role
Authentication and Authorization
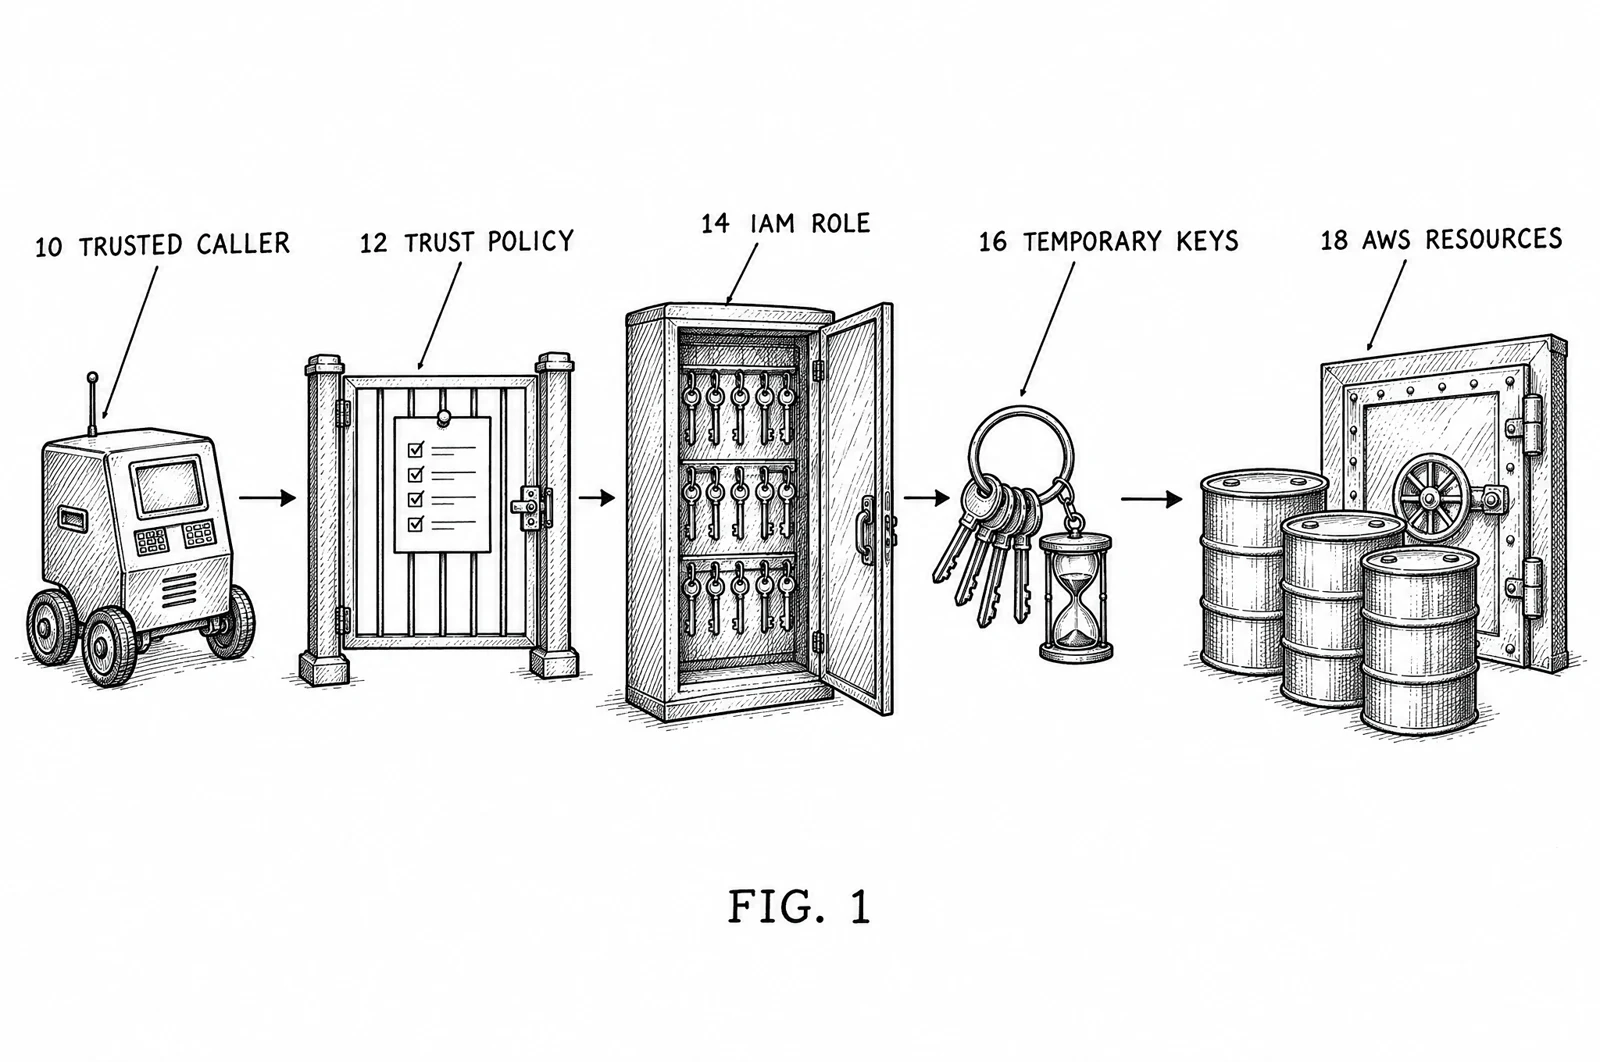
An AWS IAM Role is an identity in Amazon Web Services (AWS) that carries a set of permissions and has no password or long-term keys of its own. IAM stands for Identity and Access Management. A trusted user, service or job assumes the role and receives short-lived credentials (for example, a server that reads files from one S3 bucket). A trust policy says who may assume it, and permission policies say what it may do.
See also AWS STS AssumeRole, Kubernetes ClusterRole, Kubernetes ClusterRoleBinding, Kubernetes RBAC, Kubernetes Role, Kubernetes RoleBinding.