Kubernetes Role
Authentication and Authorization
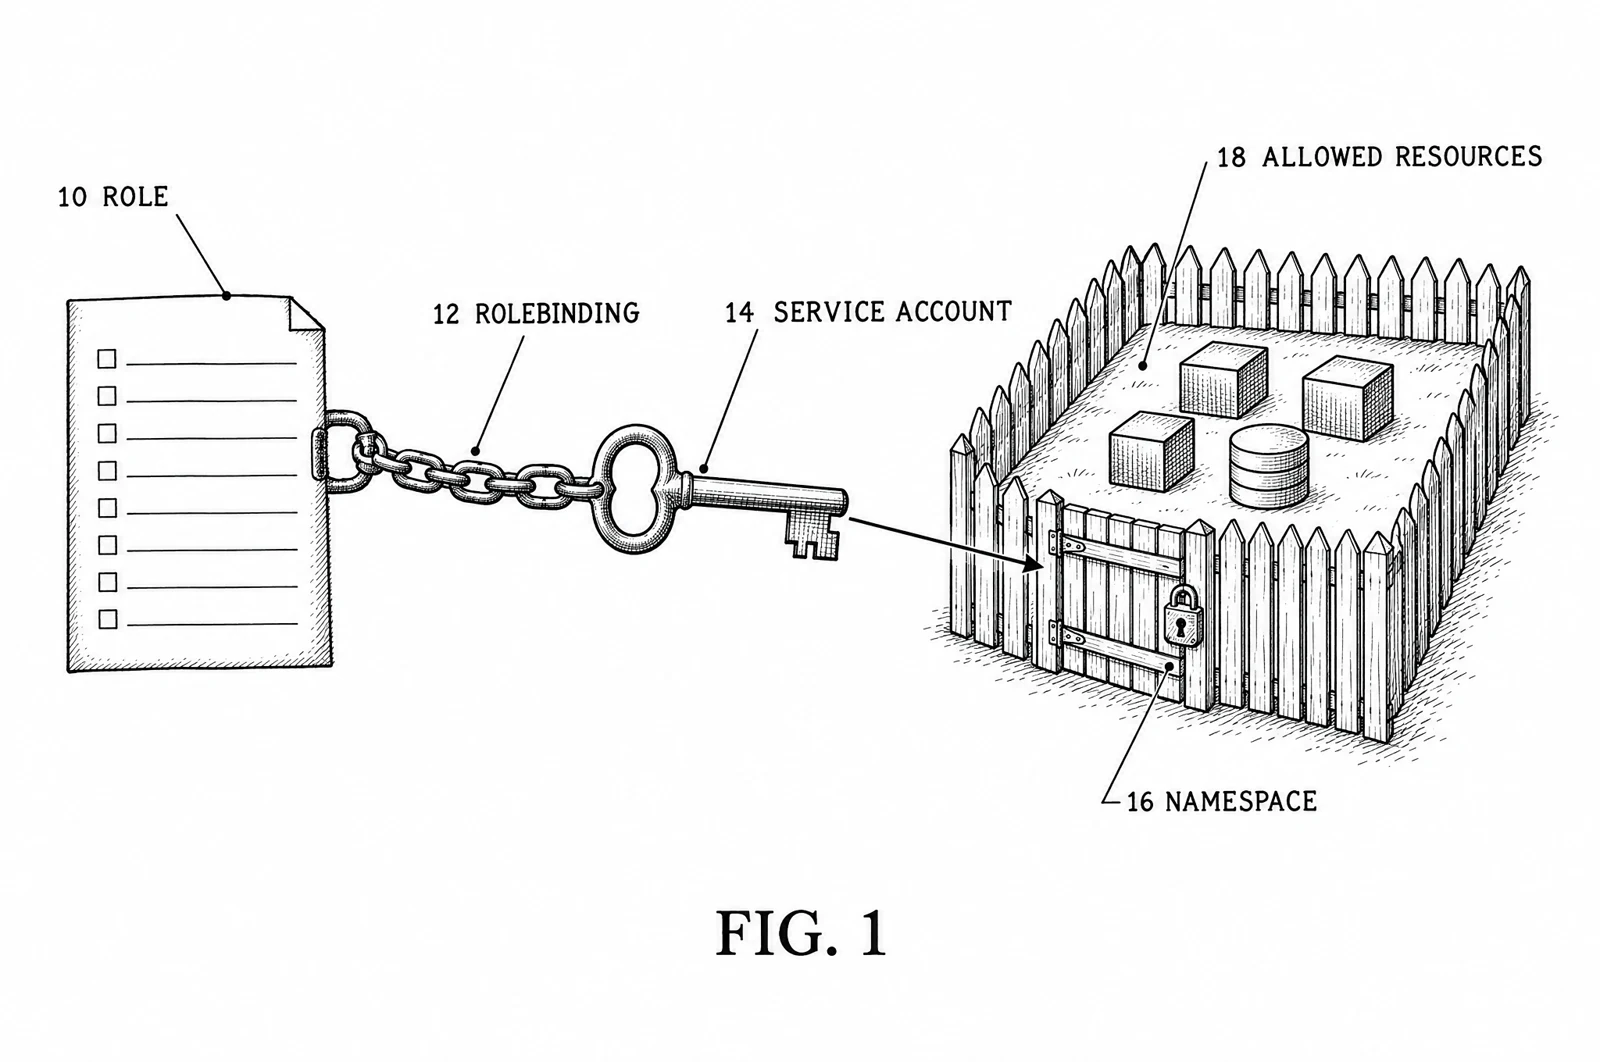
A Kubernetes Role is an access control object that lists which actions are allowed on which resources inside one namespace. It is part of role-based access control (RBAC) and contains rules such as "get and list pods" or "update deployments". A Role does nothing alone: a RoleBinding attaches it to a user, group or service account (for example, a CI account that may update deployments only in staging).
See also Kubernetes RoleBinding, Kubernetes ServiceAccount, OIDC (OpenID Connect), SAML (Security Assertion Markup Language), AWS IAM Role, AWS STS AssumeRole.