eBPF
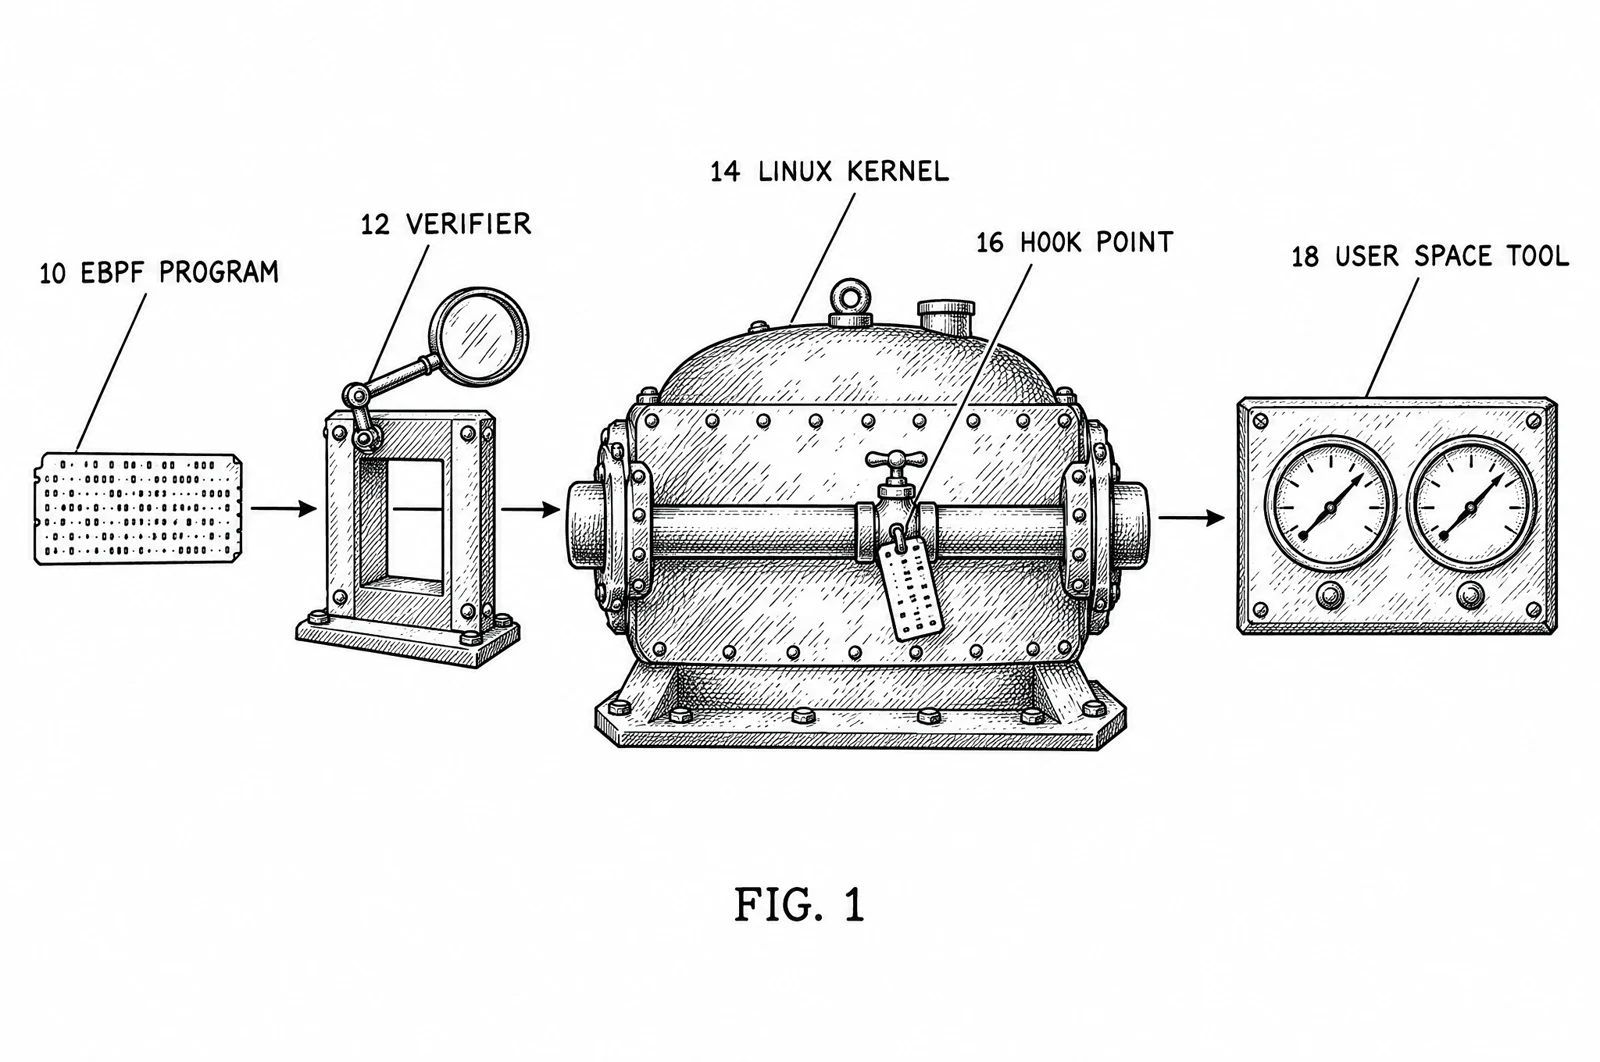
eBPF (extended Berkeley Packet Filter) is a Linux kernel feature that runs small, sandboxed programs inside the kernel. You write a program, and a verifier checks that it is safe and always finishes before the kernel loads it. The program is then attached to a hook (for example, a system call or a network packet arriving) and sends what it sees to tools outside the kernel.
See also Elasticsearch, Grafana Tempo, Log Rotation, Observability, OpenTelemetry, Prometheus.