SLSA Provenance
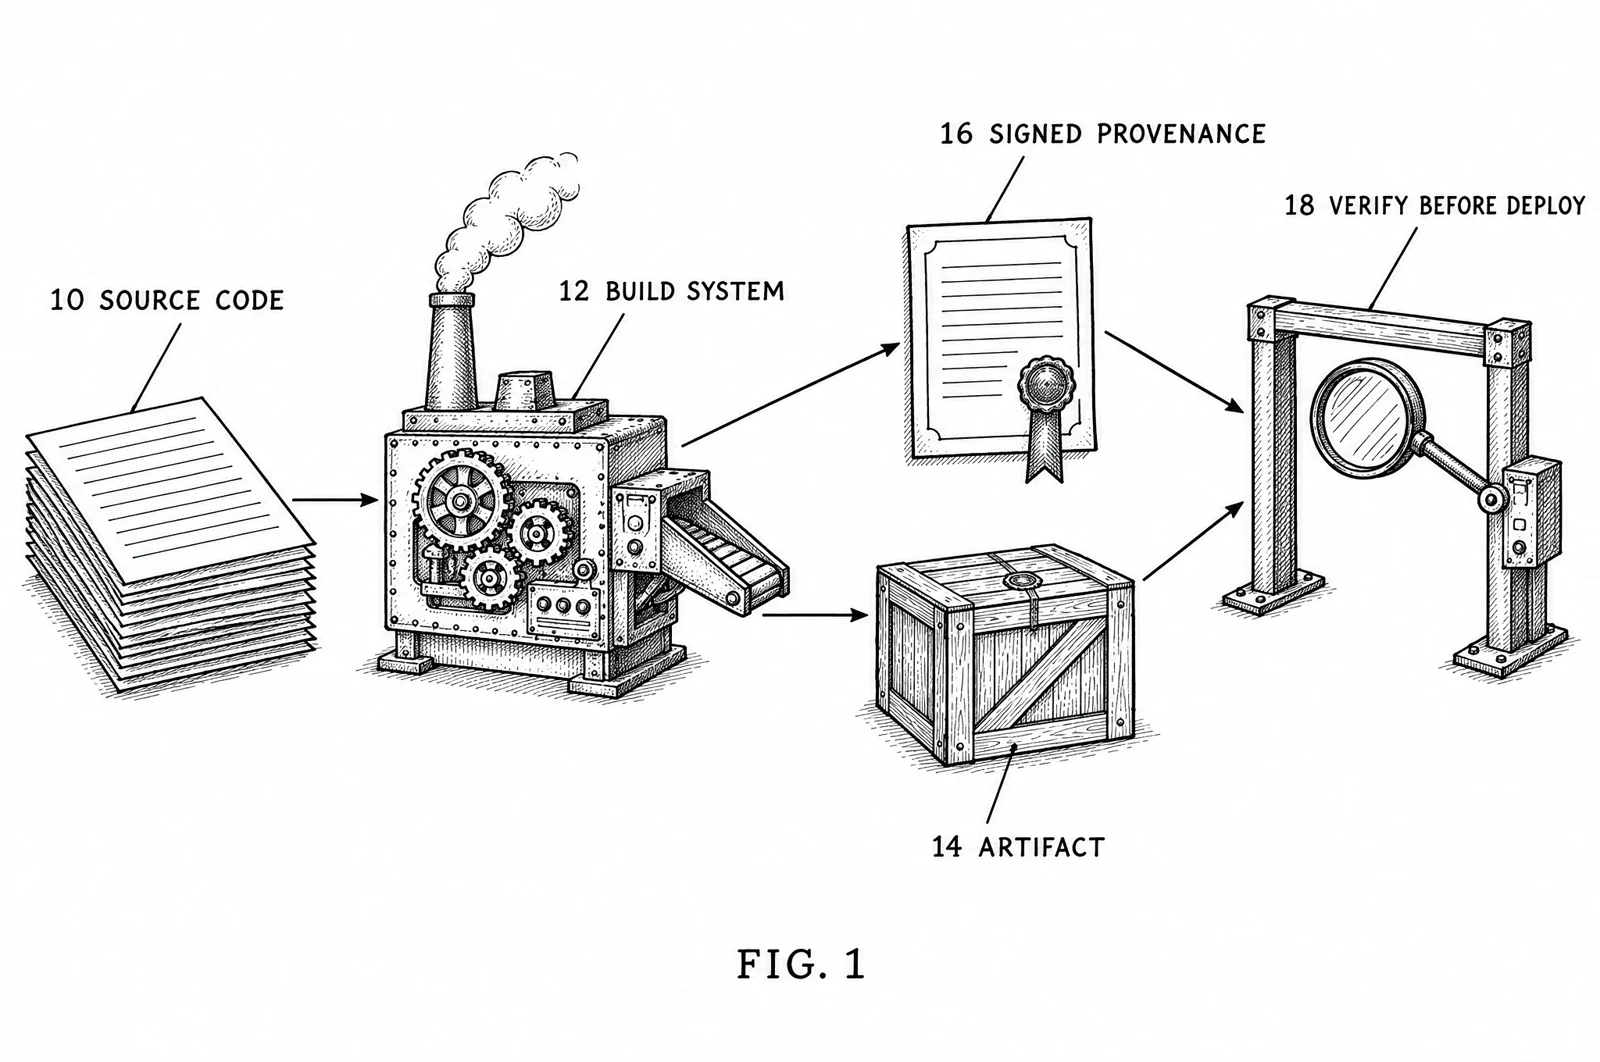
SLSA Provenance is a signed record that says where a software artifact came from and how it was built. SLSA stands for Supply-chain Levels for Software Artifacts. The record lists details such as the source repository, the commit, the build system and the digest of the output (for example, a container image). Before deploying, a policy check can verify the signature and confirm that a trusted builder made the artifact from the expected source.
See also Software Bill of Materials (SBOM), Software Supply Chain Security, SSL, Vulnerability Scanning, Zero Trust, Active Directory.